Remote support becomes much harder the moment a company stops thinking in terms of “users with laptops” and starts dealing with a real operating mix: Windows endpoints, Macs in creative or executive teams, and Linux systems running internal tools, shared workstations, or server-side workloads.
At that point, the problem is no longer distance. It is standardization.
A support team may have one ticket queue, one escalation path, and one service-level target. But underneath that operating model sit three platforms with different permission systems, different expectations around user presence, different behavior at the login screen, and different failure modes when no one is there to approve a session. The support process looks unified on paper. In practice, it fractures.
That fracture shows up in small delays that compound fast. A Windows machine can often be reached one way, a Mac requires privacy permissions to be configured another way, and a Linux system may depend on the display server, desktop environment, or whether the session is running under X11 or Wayland. The result is not simply technical inconsistency. It is lost technician time, more handoffs, more coordination with end users, and more exceptions that never quite fit the standard runbook.
One support process, three different operating assumptions
Windows, macOS, and Linux do not fail in the same way under remote support, because they were not designed with the same remote-control assumptions.
On Windows, many teams are used to a relatively mature remote administration model. That often leads to optimism. If a support workflow works well for Windows, there is a tendency to assume it will extend cleanly to everything else. It rarely does. Even on Windows, unattended access and login-screen behavior still depend on how the tool is deployed, what permissions it has, and whether the machine is being treated as a support endpoint or a general office desktop.
macOS adds a different kind of friction. Support access is shaped by Apple’s privacy and security model, especially around screen recording, accessibility, and system-level control. A tool may technically support macOS, but that does not mean the experience matches Windows once a device has been locked down by policy, managed through MDM, or handed to an executive who will not tolerate repeated prompts. Many support delays on Mac are not caused by the tool failing outright. They come from partial access: you can see the screen but cannot control it, or you can connect only after the user approves several permissions locally.
Linux is the most misunderstood part of the stack. Businesses often describe Linux support as a niche requirement until a critical system depends on it. That system may be a developer workstation, a QA machine, a kiosk, a lab device, an internal dashboard host, or a server with a graphical interface that someone eventually needs to reach quickly. The challenge is that “Linux support” is rarely a single thing. The experience changes across distributions, package formats, desktop environments, and display servers. A platform can claim Linux compatibility and still fall short in the cases that matter operationally.
This is the central mistake many teams make: they buy for nominal compatibility rather than behavioral consistency.
Why unattended access changes the economics of support
In mixed environments, unattended access is not a premium feature. It is what separates a support process from a scheduling exercise.
When unattended access is missing or unreliable, every support interaction starts with coordination. Someone has to be available. Someone has to approve the session. Someone has to stay present if the connection drops, the machine reboots, or the technician needs to reconnect after a policy change, software install, or patch cycle. That may be tolerable for occasional ad hoc support. It breaks down quickly in real operations.
Think about a few common situations:
- A support technician needs to reconnect after restarting a Windows endpoint to finish a driver or policy update.
- An operations team needs to reach a Mac outside the employee’s working hours because a business-critical application failed after an OS update.
- An admin needs persistent access to a remote Linux workstation that runs an internal tool used by several departments.
- A shared device in a lab or kiosk environment needs maintenance, but there is no dedicated user nearby to approve every session.
In each case, the real issue is not whether a remote session can start. It is whether the support process can survive interruption. Reboots, disconnects, lock screens, and user absence are normal operating conditions. Tools that require a fresh approval cycle every time turn routine work into delay.
This is also where login-screen access matters more than many buyers realize. If a technician cannot reconnect to a system until someone signs in locally, unattended support is only partially unattended. That distinction matters during maintenance windows and after restarts.
Where Linux usually breaks the cross-platform promise
Linux support is often where an otherwise reasonable remote support strategy becomes patchwork.
A company may cover Windows through RDP or a commercial support tool, handle macOS with a separate remote assistance product, and leave Linux to SSH, VNC, or a mix of scripts and institutional knowledge. That can work for highly technical teams. It works less well once Linux systems sit inside broader business operations.
SSH is excellent for command-line administration. It is not a complete answer when the machine has a graphical workload, a less technical operator, or a support scenario that depends on seeing the exact desktop state. VNC can fill part of that gap, but it often adds its own setup burden, security concerns, and inconsistent user experience across environments. Internal teams then compensate with documentation, one-off exceptions, and “the one admin who knows how this box works.”
That is expensive in ways most organizations do not measure directly. It raises mean time to resolution. It makes support quality depend on individual staff rather than process. It weakens auditability because access paths differ by platform. It also expands risk, since every extra remote method introduces another place to manage credentials, session policies, and revocation.
Linux display behavior adds one more layer. On modern Linux desktops, remote control can behave differently under X11 and Wayland. That is not a marketing nuance. It affects what a technician can actually do. If a business depends on remote access to persistent Linux systems, those differences shape deployment choices, runbooks, and support expectations from the start.
The overhead of patchwork remote support stacks
Many companies reach mixed-OS support by accumulation rather than design.
- Windows gets VPN plus RDP because that was already available.
Linux gets SSH because admins know it well.
Macs get a separate support tool because the first option was awkward.
Ad hoc user support happens over a meeting app or a lightweight remote assistance product.
Unattended access is handled by yet another tool for the subset of machines that need it.
Each individual decision can look sensible. Together, they create a support model that is harder to secure and harder to run.
Technicians need to remember which tool fits which device and which conditions. End users get different instructions depending on platform. Access logs and session controls are spread across multiple systems. Offboarding or contractor access becomes harder to audit. Training takes longer because new staff have to learn exceptions before they can learn the standard path.
There is also a governance problem here. A fragmented stack tends to produce uneven controls. One platform may have strong session auditing, another may rely on shared credentials, and a third may depend on manual steps that no one consistently documents. For SMB and mid-market teams, that inconsistency matters because support often sits close to production access.
The cost of fragmentation is not only software spend. It is the operational drag of running support without a stable, cross-platform method.
What to evaluate in a mixed-OS support platform
A useful buying framework starts with behavior, not branding.
First, check whether the platform handles Windows, macOS, and Linux as first-class environments rather than partial add-ons. “Supported” should mean support teams can onboard devices with predictable results, not merely establish a session under ideal conditions.
Second, test unattended access under realistic conditions. That means reconnecting after a restart, reaching the machine when no user is present, and confirming what happens at the login screen. If your support model includes after-hours maintenance, shared devices, or remote admin work, this is core functionality.
Third, examine permission setup and policy fit. On macOS, that includes privacy-related permissions and how manageable they are at scale. On Linux, it includes distribution coverage, package availability, and display-server behavior. On Windows, it includes the level of control available when system prompts or privileged actions appear.
Fourth, look at how the platform reduces coordination overhead. The right tool should lower the number of messages, approvals, and manual re-entry steps required to complete common tasks. Mixed-OS support fails when too much of the process depends on users being available at the right moment.
Fifth, evaluate consolidation value. A unified platform should reduce the number of parallel tools required for support, not simply become one more layer on top of an already fragmented stack. That has consequences for training, security policy, and reporting.
Where HelpWire fits
One of the real gaps in mixed-OS remote support has been Linux unattended access. Many tools can claim some form of Linux support, but that support often becomes thinner once you move beyond attended sessions or simple command-line administration.
A workable platform in this category should offer consistent support across Windows, macOS, and Linux, while treating unattended access as an operational requirement. It should also be honest about the fact that Linux is not uniform.
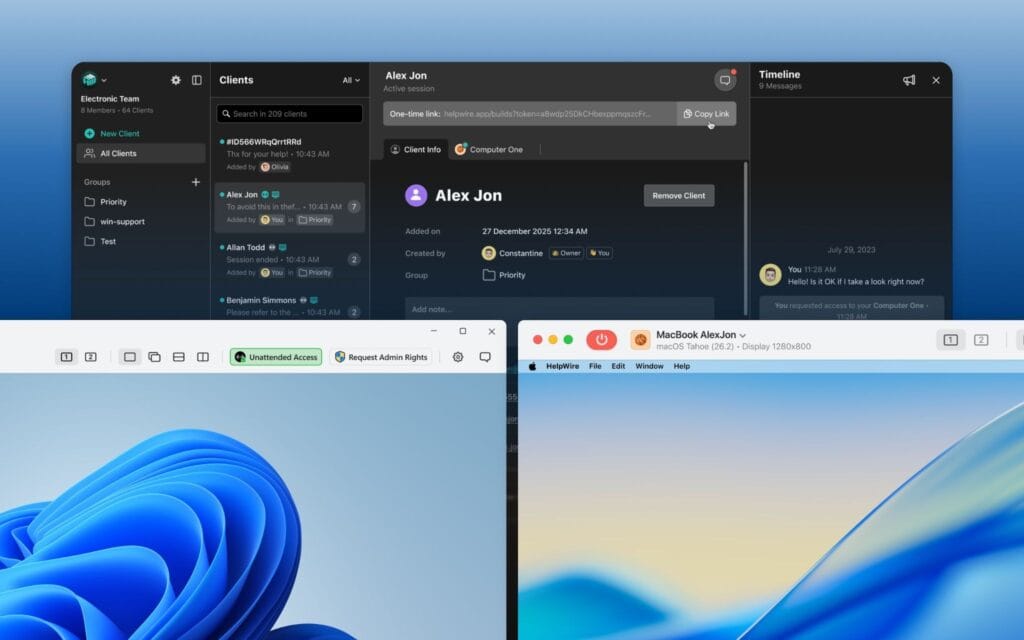
HelpWire is one example that fits that discussion. It supports remote support across Windows, macOS, and Linux, offering reliable unattended access to Linux systems, a crucial feature for cross-platform support. It supports mainstream Linux environments like Ubuntu, CentOS, and Fedora. Notably, while most long-time players in the remote support industry do not hurry to adopt Wayland display protocol, HelpWire supports both X11 and Wayland, making it a complete after-hours remote access tool.
That distinction matters. For support teams and admins, the question is not whether “Linux works.” It is whether the Linux systems they manage can be reached in the states that matter during real maintenance and support work. Persistent remote workstations, lab systems, shared machines, and internal tools often need access that survives user absence and allows reconnecting without repeated approvals. Linux unattended access closes part of that operational gap, but the X11 versus Wayland behavior still affects deployment planning and user expectations.
That makes HelpWire relevant here less because of a broad cross-platform claim and more because it addresses a specific point of friction that often forces businesses back into tool fragmentation. It will not remove the need to think carefully about Linux environment choices, permissions, and remote-access policy. But it does represent the kind of practical improvement businesses should look for when evaluating whether one platform can support a mixed-OS estate with fewer workarounds.
Mixed-OS remote support does not break because teams are remote. It breaks because businesses try to run one support process across platforms that behave differently, then fill the gaps with extra tools and manual coordination. The better approach is to treat cross-platform support as an operating-model design problem. Once that happens, the evaluation criteria become clearer: predictable permissions, reliable unattended access, realistic Linux support, and fewer exceptions embedded in the workflow. That is what reduces friction. And in support operations, friction is usually where cost hides.