
A supplier misses two shipments. Your operations lead says it's temporary. Then the supplier files for bankruptcy protection, customer orders pile up, and your sales team starts discounting just to keep accounts from leaving. Nothing in that chain of events is unusual. What's unusual is how many leadership teams still treat it as bad luck instead of a failure of strategy.
A risk management strategy exists for moments like that. Not as a binder on a shared drive, and not as a compliance exercise owned by one department, but as a management system for making better decisions under uncertainty. It tells you which risks matter, which ones don't, who owns them, how much exposure the business is willing to carry, and what action gets funded before a threat turns into a disruption.
Boards often ask for growth plans, margin plans, and transformation plans. They should ask for the same level of clarity on risk. A company that can't explain how it identifies, prioritizes, and treats uncertainty is not managing strategy. It's managing surprises.
What Is a Risk Management Strategy Really
A fast-growing company usually feels strong right before risk becomes visible. Revenue is up, hiring is active, customers are coming in, and operating assumptions start to harden into habits. Then one external shock exposes how little of that momentum was protected.
That's the practical meaning of a risk management strategy. It is the operating discipline that reduces strategic surprise. It helps leaders identify threats early, assess their business consequences, choose a response, and keep watch as conditions change.
It's a decision system, not a document
Most executives have seen risk registers that go nowhere. They contain categories, color coding, and broad statements like “monitor supplier concentration” or “review cyber posture.” Those lists aren't strategy unless they change real decisions.
A real risk management strategy answers questions like these:
- What could stop our objectives from being achieved this year?
- Which exposures are worth funding against because they threaten revenue, continuity, or trust?
- Which risks can we tolerate because treating them would cost more than carrying them?
- Who decides and who acts when indicators move in the wrong direction?
If your team needs a starting point for that conversation, this practical guide to identifying major risks is useful because it pushes leaders to look beyond obvious operational issues and map risk to strategic choices.
Value protection is only half the story
Good boards understand that risk management doesn't only prevent losses. It also improves capital allocation. When leaders know the exposure behind a product launch, market entry, vendor dependency, or data practice, they can choose faster and with more discipline.
Board lens: A company with a weak risk process often mistakes optimism for capability.
That distinction matters. Risk management strategy is not about avoiding ambition. It's about making ambition survivable.
Why Your Business Cannot Afford to Ignore Risk
Executive confidence can be dangerously misleading. A leadership team may feel prepared because major incidents haven't happened yet, reporting lines look clean, and no one is raising alarms. That kind of confidence often reflects calm conditions, not actual resilience.
The gap shows up clearly in FIS Global's 2025 risk management findings. 95% of U.K. leaders reported confidence in managing risks, compared with 90% in the U.S. and 87% in other regions. Yet the same report found that 58% of global leaders identified economic conditions as a top risk, while 61% identified attracting and retaining talent as a primary concern. Confidence and exposure were moving in different directions.
Confidence is not a control
For a board, that data should trigger one conclusion. Management sentiment is not evidence of readiness. If the organization feels confident while major external and talent pressures remain dominant, then the issue is not morale. It is whether the company has translated awareness into treatment plans, ownership, and monitoring.
That's where formal strategy matters. It forces leaders to move from “we know the risk” to “we know what we'll do about it.”
A business that ignores this discipline pays in several ways:
- Slower decisions: Teams debate assumptions during a crisis because risk ownership was never defined.
- More volatile operations: Supply, staffing, legal, and technology issues hit harder when no contingency path exists.
- Weaker investor confidence: Capital providers want evidence that management can protect downside, not just pursue upside.
- Reputational fragility: Customers forgive disruption more easily when they see competence, transparency, and continuity.
Risk management affects performance, not just protection
The strongest reason to invest in a risk management strategy is that it changes business quality. It improves how leaders prioritize, where they place buffers, which dependencies they reduce, and when they stop treating temporary workarounds as permanent solutions.
A useful way to frame this at the board level is preparedness as a competitive capability. The argument is well captured in this perspective on why preparedness is a competitive advantage in business. Companies that anticipate disruption don't merely defend themselves better. They reallocate faster while competitors are still diagnosing the problem.
Preparedness doesn't remove uncertainty. It lowers the price you pay when uncertainty arrives.
That's why risk management belongs in strategy reviews, operating reviews, and resource allocation discussions. If it lives only in audit or compliance, the business will notice it only after damage has already started.
The Core Components of a Risk Management Framework
A useful framework works like a ship's navigation system. It doesn't assume one perfect route and forget the sea. It constantly checks conditions, updates the route, and tells the crew when a small drift has become a strategic problem.
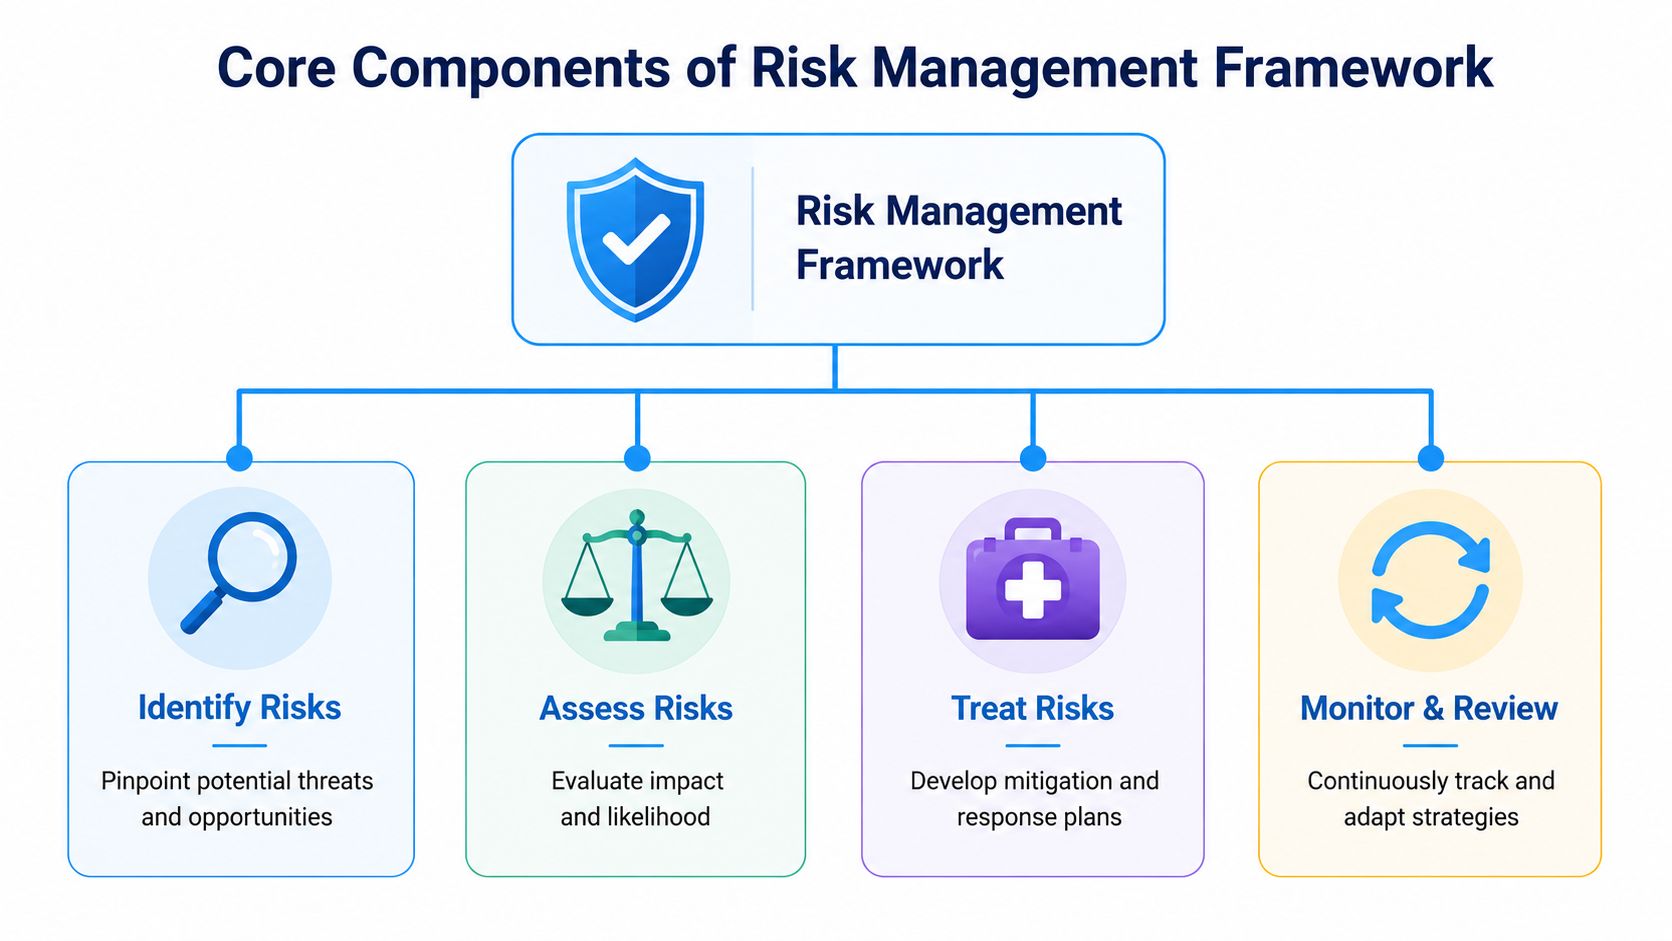
That's how a risk management framework should work inside a business. The core loop is simple: identify, assess, treat, and monitor. The simplicity is deceptive. Most companies fail not because the model is unclear, but because they treat it as a yearly checklist instead of a continuous operating cycle.
Identify risks
Risk identification means naming the events, dependencies, and assumptions that could affect objectives. That includes obvious categories such as suppliers, cyber exposure, regulation, liquidity, hiring, and reputation. It also includes strategic risks that management teams often miss, such as concentration in one customer segment, overreliance on a single channel, or key person dependency.
Many firms benefit from linking risk to capability. A company map of what the business must be able to do, such as deliver, sell, serve, comply, and retain talent, often surfaces weak points faster than generic brainstorming. That makes business capability mapping especially useful in risk identification.
Assess risks
Once the risks are named, leaders need to evaluate them by likelihood and impact. The point isn't mathematical precision for its own sake. The point is to distinguish noise from exposure that can materially alter performance.
A board-level discussion should ask:
| Question | Why it matters |
|---|---|
| Could this disrupt revenue or delivery? | It connects risk to performance. |
| How quickly could it materialize? | It determines response time and governance. |
| Do we have early indicators? | It separates monitorable risk from surprise risk. |
| Is this isolated or systemic? | It reveals whether one event can trigger wider failure. |
Treat and monitor risks
Treatment is where strategy becomes visible. Some risks are avoided, some reduced, some transferred, some accepted, and some require contingency planning. Those choices must be explicit.
Monitoring keeps the framework alive. If leaders don't review indicators, test assumptions, and adjust actions, the framework decays into reporting theater. This is why mature enterprise programs often align risk work closely with strategy and performance management. For boards that want a stronger governance model, this explanation of COSO ERM integration with strategy is a practical reference point.
Practical rule: If a risk has no owner, no trigger, and no review cadence, it isn't being managed. It's being described.
Five Powerful Ways to Treat Business Risks
Once a risk is assessed, management has to decide what to do with it. At this stage, many teams default to mitigation and stop thinking. That's too narrow.
Modern practice recognizes five primary treatment options. The model expanded from the classic four responses to include contingency planning as a standalone strategy, a shift linked to the complexity of global supply chains and cyber threats, as outlined in Optro's discussion of modern risk treatment options.
The five options side by side
| Treatment option | What it means | Best used when | Example |
|---|---|---|---|
| Avoidance | Eliminate the exposure entirely | The upside isn't worth the risk | Declining to enter a market with regulatory conditions the firm can't support |
| Reduction | Lower the likelihood or impact | The risk is real but manageable | Adding supplier qualification steps and dual approval for critical purchasing |
| Transference | Shift part of the risk to another party | Another party can absorb or manage it better | Using cyber insurance or contractual indemnities with a vendor |
| Acceptance | Retain the risk knowingly | The exposure is limited or treatment isn't economical | Accepting minor defects in a non-core internal tool |
| Contingency planning | Pre-plan an alternate response | The risk can't be fully prevented | Preparing a manual operating process if a core platform fails |
The mistake boards often make
Boards often ask whether management has “mitigated the risk.” That phrasing can narrow the conversation too early. Some risks shouldn't be mitigated. They should be avoided. Others can't be reduced enough, so the strategic question is whether a fallback plan exists.
Consider two examples.
A company dependent on one overseas manufacturer can reduce risk by improving oversight, safety stock, and communication routines. But if concentration remains structurally dangerous, avoidance may be the better long-term treatment through supplier diversification or redesigning the product for broader manufacturability.
A software company handling sensitive customer information can add controls, buy insurance, and train staff. Those are valid reduction and transference tools. But if a critical system still goes down, only contingency planning answers the board's next question: how will the company keep serving customers tomorrow morning?
Choosing among them
Leaders should match treatment to business reality, not habit.
- Use avoidance when the risk threatens core viability.
- Use reduction when operational changes can materially lower exposure.
- Use transference when a counterparty can carry the burden more efficiently.
- Use acceptance when the cost of treatment exceeds the value protected.
- Use contingency planning when interruption is possible even after the other treatments are applied.
The strongest treatment plans often combine several of these. What matters is that each choice is deliberate.
How to Build Your Risk Management Strategy Step by Step
Most companies don't need a bigger theory of risk. They need a build sequence. The work becomes manageable once leadership stops treating it as a giant enterprise project and starts treating it as an operating discipline with named owners, recurring decisions, and clear reporting.
A straightforward implementation path is enough to get started.

1. Define context and risk appetite
Start with business objectives, not risk categories. What must the company achieve, protect, and preserve over the planning period? Revenue continuity, customer trust, regulatory standing, product delivery, and talent retention usually belong on that list.
Then define risk appetite. That means clarifying where the company is willing to take risk and where it is not. A firm may accept experimentation in product development but have very low tolerance for compliance failures or single points of failure in operations.
2. Assign ownership
Risk management fails when everyone participates but no one owns. Create a small governance structure. In larger firms, that may be a risk committee with senior functional leaders. In smaller businesses, it may be the CEO, finance leader, operations head, and technology lead meeting on a fixed cadence.
The key is clarity:
- Executive sponsor: Sets expectations and resolves trade-offs.
- Functional owners: Identify and treat risks inside their domains.
- Coordinator: Maintains the register, follows up on actions, and prepares reporting.
3. Run a structured risk workshop
Bring leaders together and force specificity. Ask each function what could interrupt objectives, what assumptions the plan depends on, where the company is concentrated, and which risks are becoming harder to monitor.
Don't let the discussion stay abstract. Push each risk statement into this format: event, cause, consequence. “Supplier disruption” is vague. “Failure of the sole packaging vendor could delay shipments and reduce service levels” is actionable.
This is also where a simple planning format helps teams move from conversation to execution. A strategic roadmap template can help translate risk priorities into timelines, ownership, and review points.
To support that build process, this walkthrough is worth reviewing:
4. Build a usable risk register
A good risk register should be short enough to drive action and detailed enough to support decisions.
Include fields such as:
- Risk statement
- Business objective affected
- Owner
- Likelihood
- Impact
- Current treatment
- Additional actions required
- Early warning indicators
- Review date
5. Implement treatment plans
At this stage, resource allocation becomes concrete. Some actions require spending, some require policy changes, and some require redesigning a process or dependency. Not every risk deserves the same intensity of treatment.
The quality of a risk strategy is visible in budgets, contracts, staffing choices, and process design. Not in presentation slides.
6. Establish reporting and review
Set a rhythm. Monthly for volatile operational risks. Quarterly for board-level review. Immediate escalation for triggers that exceed tolerance.
The discipline is simple. Review what changed, whether treatment is working, whether exposure has increased, and whether new risks need board attention. That cadence is what turns a one-time workshop into a functioning risk management strategy.
Risk Management Strategies in the Real World
Frameworks matter, but boards usually understand risk best through operating stories. The same discipline looks very different in a software company than it does in a product business with physical inventory and supplier dependencies.
SaaS startup
A growing SaaS company often starts with one dominant concern, product velocity. Risk enters later through the side door. Customer data accumulates, enterprise clients ask harder security questions, a few engineers become critical points of dependency, and the leadership team realizes that a service interruption would be both an operational issue and a trust issue.
Its strategy might include tighter access controls, clearer incident response ownership, vendor review for core infrastructure, and a contingency plan for platform outages. But a sharper board would ask another question: are there product or data practices creating avoidable exposure in the first place? That's where the company moves beyond control implementation and begins reducing risk at the source.
Consumer packaged goods company
A mid-sized CPG business faces a different profile. It depends on manufacturers, packaging vendors, freight, retail timing, and consumer demand shifts. A single disruption can cascade across production, shelf availability, and working capital.
Its risk management strategy might emphasize supplier diversification, alternate packaging specifications, inventory buffers for critical inputs, and tighter communication between procurement, finance, and sales. Store security or cyber controls may still matter, but the larger strategic issue is dependency concentration. The company's resilience depends less on elegant policy and more on how many single points of failure remain in the operating model.
Same framework, different strategic choices
Both companies use the same risk cycle. They identify, assess, treat, and monitor. What changes is the design of the response.
That's the point boards should keep in focus. Risk management strategy is not a standard template to be copied across industries. It is a discipline that must reflect the economics, dependencies, and failure modes of the business in front of you.
Common Pitfalls and Advanced Risk Reduction Tactics
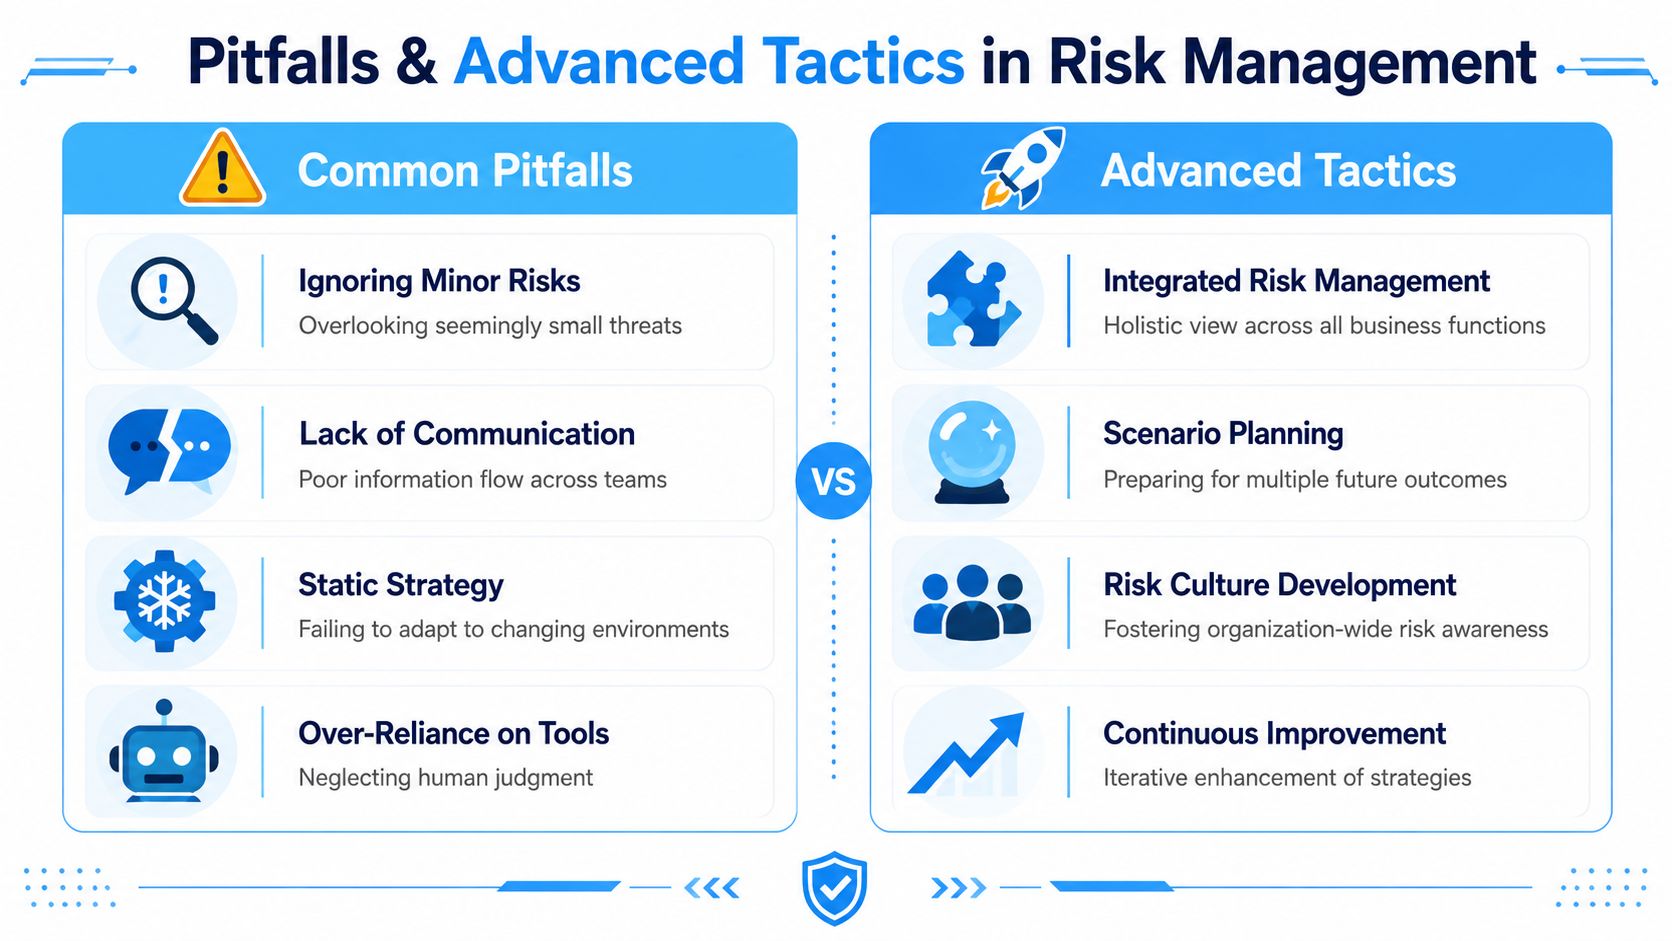
Most weak risk programs don't fail because leaders ignore risk entirely. They fail because leaders manage it in ways that feel responsible but don't materially change exposure.
Three mistakes show up repeatedly.
Common failures
- Compliance-only thinking: The organization documents risks for audit purposes but doesn't use the process to shape strategic choices.
- Template dependence: Teams import generic categories without tailoring them to the company's actual business model, concentration points, or operating constraints.
- Leadership distance: Senior executives delegate the topic downward, then act surprised when unowned risks become executive crises.
These are governance problems, not documentation problems.
The blind spot in most treatment plans
Many businesses default to controls. If there is data risk, add more security controls. If there is fraud risk, add approvals. If there is driver safety exposure, add monitoring. Controls matter, but they often manage symptoms instead of reducing the source of risk.
That blind spot is captured well in Phil Venables' argument for alternative risk strategies built on inherent reduction and threat neutralization. His core point is strategically important: many businesses over-rely on controls while overlooking inherent risk reduction, meaning the elimination of the risk source itself. A clear example is data minimization, where a business reduces the attack surface by collecting or retaining less sensitive data to begin with.
The same logic applies far beyond cybersecurity. Fleet-heavy businesses, for example, can learn from operational approaches built around behavior and root-cause visibility rather than only post-incident enforcement. Practical driver behaviour insights illustrate the broader principle. When you change the conditions that create exposure, you need fewer layers of response later.
The best risk treatment is often subtraction, not addition.
What advanced leaders do differently
They ask better questions:
- Can we remove the exposure entirely?
- Can we simplify the process that creates the risk?
- Can we reduce dependency on a single vendor, data set, route, or person?
- Are we adding controls because they work, or because redesign feels harder?
That's the strategic upgrade most companies need. Not more controls by default, but more willingness to redesign reality so the risk has less room to exist.
The clearest strategy work happens when leaders can connect business models, capabilities, market dynamics, and risk choices in one view. The Business Model Analyst publishes practical analysis for executives, consultants, founders, and educators who need that level of strategic clarity.