
The memorandum creates a new class of licensed operator, then declines to name a fee, an indemnity, or an appropriation. The one dollar figure in the document is a $1 million bond the participant puts up against itself.
On 12 August, President Trump signed a national security memorandum letting vetted American companies run surveillance and disruption operations against foreign cybercrime groups, under Justice Department and Homeland Security control. The document authorizes the work and never prices it. There is no fee schedule, no indemnity, no appropriation, and one number: a minimum $1 million bond or escrow the company forfeits if it breaches its contract. Under those terms the operations cannot be the product. The credential is.
A defense contractor who wants to launch a rocket has to show the FAA it can cover up to $500 million in third-party liability, and Congress built a federal indemnification tier above that. A company that wants to remotely degrade or destroy a foreign criminal group’s systems on Washington’s behalf has to post a million dollars and read Section 5(c), which says the memorandum creates no right enforceable against the United States by anybody. Both activities are dangerous, both are licensed, both are done at the government’s direction. Only one comes with a balance sheet behind it.
What Happened
The memorandum, “Expanding Capabilities to Combat Transnational Cyber-Enabled Crime,” landed on the White House site late Wednesday. It directs the National Coordination Center to build a Program authorizing “Participating Companies” to conduct Cyber Surveillance Operations and Cyber Effects Operations against foreign Cyber-Enabled Transnational Criminal Organizations, which the document shortens to CE-TCOs.
The definitions carry the weight. A Cyber Effects Operation covers activity that results in “the manipulation, disruption, denial, degradation, or destruction” of information systems, networks, the physical or virtual infrastructure they control, or the data on them. A Cyber Surveillance Operation means accessing systems without the owner’s authorization to collect intelligence, including intelligence for future effects operations, while staying undetected.
Two Program Executive Directors, one designated by the Attorney General and one by the Secretary of Homeland Security, approve every operations package in writing before anyone acts. They cannot approve anything likely to produce a “Critical Outcome,” defined as loss of life, serious injury, or conduct rising to the use of force or armed attack under international law. Companies sign contracts with DOJ or DHS and pass vetting on technical proficiency, proven performance of cyber operations, facility security and personnel screening. The operating procedures are due in 60 days, the first program report in 180.
The White House put American consumer losses to cyber-enabled crime at more than $20.8 billion in 2025. The FBI’s Internet Crime Complaint Center reported $20.877 billion across 1,008,597 complaints that year, a 26% increase and an average loss of $20,699.
The Backstory
Private companies have been dismantling criminal infrastructure for fifteen years. They did it through civil courts. Microsoft’s Digital Crimes Unit says it has disrupted 32 malware families and nation-state actors through civil actions and reclaimed more than 500 million victim devices. In May 2025 the unit got an order from the Northern District of Georgia and seized roughly 2,300 domains behind Lumma Stealer, which Microsoft had found on about 394,000 Windows machines, while DOJ took the sales infrastructure and Europol and Japan’s Cybercrime Control Center handled their jurisdictions. In December 2023 a judge in the Southern District of New York let Microsoft seize the infrastructure of Storm-1152, a Vietnamese operation that had generated something on the order of 750 million fraudulent Microsoft accounts.
That model has an income statement behind it. Microsoft sues on its own trademarks and its own platform harm, so the legal spend defends the product. The company owns the injury it is litigating.
The legal barrier for everyone else stayed where it has been since 1986. Lawyers at Crowell & Moring, writing on Lawfare in May, concluded that absent explicit government authorization or a law enforcement partnership, a company should treat neutralizing attacker infrastructure as off limits. Trump’s March National Cybersecurity Strategy floated a bigger private role in offensive operations and stopped short of building one. This memorandum builds it.
The Plan
The National Coordination Center runs the program. That center was created under Section 6(d) of Executive Order 14159, the January 2025 immigration enforcement order, and sits inside the Homeland Security Task Force.
Participation requires a contract with DOJ or DHS, disclosure to the NCC of every commercial relationship entered under the program, annual re-evaluation, and a stop-and-report obligation the moment a company finds it has touched a US person or a US-based system. DOJ and DHS may condition the contract on a bond or escrow of “not less than $1 million,” forfeited on non-compliance. The eligibility criteria are supposed to admit large firms for capacity and small ones for specialized tasks.
One clause describes commerce, and it runs in a single direction. Participating Companies may enter agreements with other private entities, from which they may receive threat information gathered in those entities’ ordinary business, and with federal, state, local, tribal and territorial agencies that will identify CE-TCO threats to them. Companies take information in and propose operations to the NCC. Nothing in the memorandum describes anyone selling anything out.
The Business Model Angle
Start with what a participant pays. A bond of at least $1 million in dead capital. Facility security and cleared personnel. Disclosure of its commercial relationships to a federal coordination center. A yearly review it can fail. Written approval on every package, which puts government latency inside its operating tempo. Then read what it receives. Authorization, subject to the availability of appropriations under Section 5(b), and Section 5(c) confirming that none of this creates a right or benefit enforceable at law against the United States. Washington’s side of the arrangement is unenforceable by design.
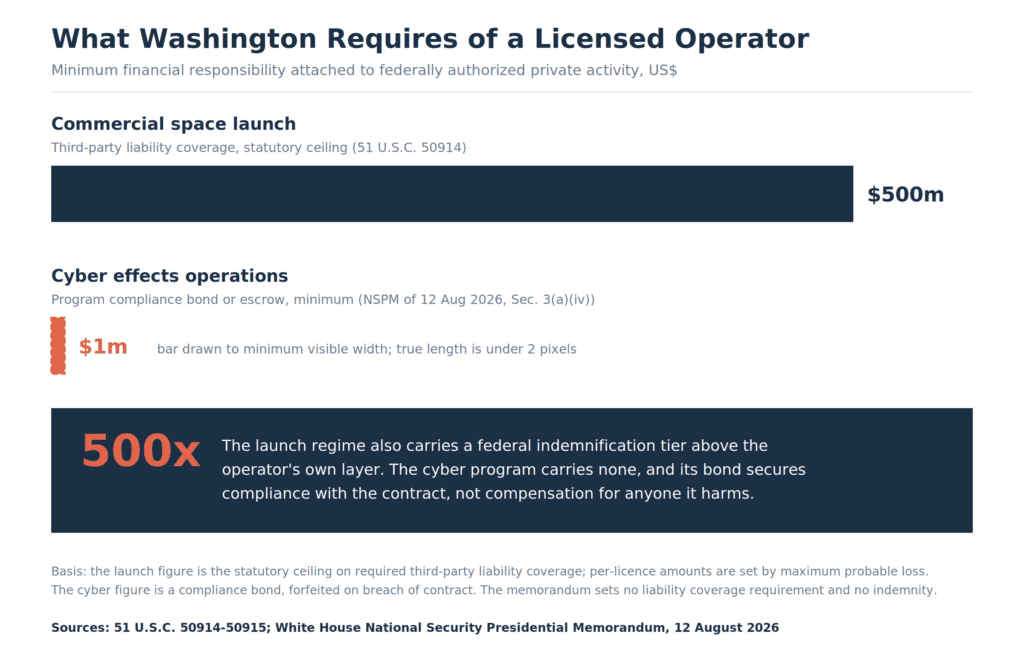
The comparison is uncomfortable because the two instruments are not the same thing, and that is the finding. The launch figure is liability coverage: money set aside to compensate people the operator hurts, sized per licence by maximum probable loss, with a federal tier above it under 51 U.S.C. 50915. The cyber figure is a compliance bond: money the government keeps if the company breaks its contract. It protects the program from the operator. Nothing in the memorandum protects anyone from the program.
Run the P&L and the offensive work does not close on its own. So the money has to sit somewhere else, and there are three places it can sit.
The first is the contract the program already requires. Entry means a signed agreement with DOJ or DHS and a completed facility and personnel review, which is most of the cost of becoming a federal supplier in the first place. Firms that were going to chase that work anyway get the on-ramp subsidized by a program they can treat as marketing.
The second is the data. The one commercial clause in the document authorizes an inbound threat-intelligence supply chain and requires participants to disclose every contract that feeds it. What the program assembles, underneath the operations, is a state-supervised aggregation layer with private companies as collection nodes and the NCC holding a map of who supplies whom. Threat intelligence is already a subscription business. This makes participants the buyers of record for a lot more of it.
The third is the credential. “Vetted by the Department of Justice and the Department of Homeland Security to conduct authorized cyber operations” is a sentence no competitor can write without joining. In US federal, state and regulated-enterprise procurement, that sentence sells.
Notice what the program removes. Microsoft’s civil actions work because Microsoft is the victim. A Participating Company acts against harm done to somebody else, on a target the government picked, with no fee and no claim. Cutting the operator loose from the injury is what takes the business case out of the operations and puts it in the badge.
The Risk
The badge prices differently outside the United States, and Washington wrote the pricing rule itself.
On 20 June 2024 the Commerce Department’s Bureau of Industry and Security issued the first final determination ever made under Executive Order 13873 and barred Kaspersky from selling cybersecurity and antivirus products to US persons. The stated basis was the Russian government’s offensive cyber capability and its capacity to influence or direct Kaspersky’s operations. Not proof of misuse. Capacity to direct. Commerce added three Kaspersky entities to the Entity List, Treasury put twelve executives on the SDN list, and the company began winding down its US business within a month.
Now apply that test to a firm that has signed a contract with DOJ, posted a bond, cleared its facilities, and disclosed its commercial relationships to a federal coordination center. A procurement officer in Brussels, Riyadh or São Paulo does not have to prove anything. The United States already established that the standard is influence, not evidence.
The firms with the capability are the firms with the exposure. CrowdStrike booked $1.27 billion of international revenue in fiscal 2025 against $3.95 billion total. Palo Alto Networks took 32.7% of its $9.22 billion fiscal 2025 revenue from EMEA and Asia-Pacific. A pure-play federal contractor has almost nothing to lose by joining. A global security vendor is being asked to trade a third of its addressable market for a credential that only sells at home.
The legal exposure sits underneath that. The memorandum does not amend the Computer Fraud and Abuse Act, because a president cannot. It instructs the program to operate in accordance with 18 U.S.C. 1030, which leaves the whole structure resting on the argument that the statute’s law enforcement carve-out reaches private delegatees. No appellate court has ruled on it. State computer crime statutes in New York, California and Virginia are untouched. A security executive quoted by CSO Online put it plainly: the commercial company has neither immunity nor indemnity that anyone can find in the memorandum, and none of the protection from retaliation that a federal agency carries.
Then there is the presumption. Section 4(c) says a foreign group will be assumed not to be part of a foreign government, or wholly directed by one, unless clear intelligence establishes the link. The company proposing the operation does not hold that intelligence. State Department officials said earlier this year that many of the Chinese gangs running Southeast Asian scam compounds trace back to Chinese government projects. If the presumption fails, the private operator is the party that hit a state.
The case against this reading deserves room. Contractors have run offensive cyber operations for the US government for years under ordinary cost-plus arrangements, and this program formalizes a channel rather than inventing one, which means the revenue mechanism may already exist in the contracting system and did not need restating in a memorandum. The operating procedures due in October can add indemnification by contract, and “not less than $1 million” reads like a floor written for the smallest specialized shop rather than a ceiling for a prime. And a firm whose customers are American banks, hospitals and utilities may find the credential worth more at home than the EMEA pipeline it puts at risk. Those are real arguments. They all depend on documents nobody has seen.
Quick Questions
Can any company hack back now? No. Only firms accepted into the program, acting on a specific operations package approved in writing by both Program Executive Directors, against a foreign target the government has designated.
Who pays for the operations? The memorandum does not say. Section 5(b) makes everything subject to available appropriations, and no appropriation accompanies it.
What does the $1 million bond cover? Compliance with the company’s contract. The government keeps it if the company breaches. It is not liability coverage and no victim has a claim on it.
Why would a company join? For the DOJ or DHS contract that entry requires, for access to the threat-intelligence flows the program authorizes, and for a vetting status competitors cannot claim.
What is the biggest commercial risk? Being treated abroad the way the United States treated Kaspersky in 2024, on the test the United States wrote.
The Business Model Analyst Take
Governments buy private capability in one of two ways. They pay for it, which produces contractors, or they license it and let the operator keep the prize, which produced privateers. This memorandum does neither. It licenses the activity, keeps the target selection, names no price, and asks the operator to post capital first.
Arrangements structured that way still get taken up, because the licence itself becomes the asset. That is the part worth watching over the next 60 days, while DOJ and DHS write the operating procedures. If the guidance adds an indemnity and a fee schedule, this becomes a normal defense line of business with unusual optics. If it adds neither, the roster of Participating Companies will tell you exactly what the badge is worth, and to whom. Expect it to fill with firms whose revenue never leaves the country, and expect the names with real international books to send a subsidiary, a lawyer, or nobody.